
Network ACL
In this article:
Network ACL#
General information#
Network access control lists (Network ACL, NACL) act as firewalls at the subnet level. When a VPC is created, a default network access control list is created. It is assigned to each subnet being created and allows all inbound and outbound traffic. The corresponding rules are shown in the tables below.
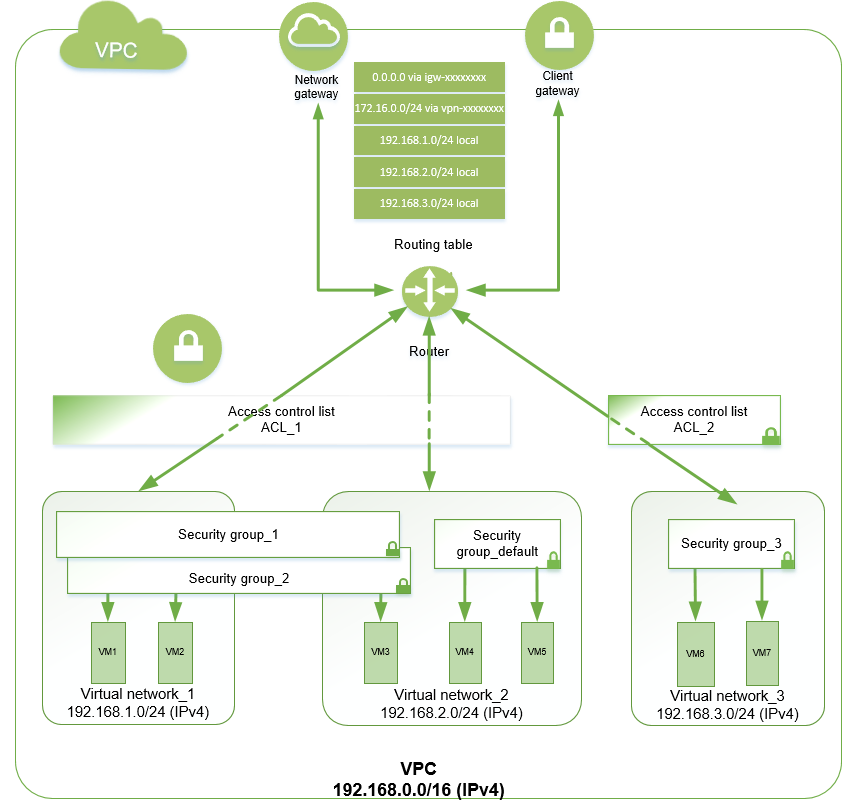
After a subnet is created, you can assign your own network access control list to it. The figure shows the possible ways to assign NACLs to subnets and security groups to network interfaces. For example, you can associate a network access control list with several subnets.
Rule number |
Protocol |
CIDR |
Ports |
Action |
|---|---|---|---|---|
100 |
all(-1) |
0.0.0.0/0 |
Allow |
|
32767 |
all(-1) |
0.0.0.0/0 |
Deny |
Rule number |
Protocol |
CIDR |
Ports |
Action |
|---|---|---|---|---|
100 |
all(-1) |
0.0.0.0/0 |
Allow |
|
32767 |
all(-1) |
0.0.0.0/0 |
Deny |
Attention
If a network access control list is assigned to a subnet that is attached to a transit gateway, inbound NACL rules will not be applied to traffic coming from the transit gateway.
Billing#
Network access control lists are not charged.
Available quotas#
The following default quotas are allocated to network access control lists:
200 NACLs in one VPC;
20 rules in one NACL in each direction.
If necessary, you can increase quotas. To do this, contact the support service via the support portal or by email support@k2.cloud.
Operations with network access control lists#
Create an NACL#
Go to Virtual machines Security Network ACL.
Click Create.
In the window that opens, set the following parameters:
Name tag (optional);
VPC in which you need to create a network access control list.
If you need to set tags, go to the next step by clicking Add tags. Specify the tag key and value.
After setting all the required parameters, click Create.
The created list will contain two rules that deny all inbound and outbound traffic, but they will have the lowest priority. Follow the link with the network access control list ID to set your own rules, assign the NACL to subnets, view the list of associated subnets, and see general information about this NACL.
Assign an NACL to a subnet#
Go to Virtual machines Security Network ACL.
Select the NACL in the resource table.
Click Associate with subnets.
In the window that opens, select the subnets to which the network access control list should be assigned.
Note
To narrow down the NACL search, you can use the VPC selector and the table search. You can select several subnets at once. Only one NACL can be assigned to a subnet; you can always associate another NACL with the subnet later.
Note
To associate another NACL with a subnet, it is enough to assign it to the subnet.
Click Assign.
You can also perform this operation on the NACL page. To do this, go to the Subnets tab and click Assign to subnets.
If you want to know which subnets a specific network access control list is assigned to, open the Subnets tab on its page.
Delete an NACL#
Important
Before deleting a network access control list, make sure that it is not assigned to any subnet. If the network access control list being deleted is associated with a subnet, first assign another NACL to it.
Go to Virtual machines Security Network ACL.
Select the NACL in the resource table and click Delete.
In the window that opens, confirm the deletion.
You can also perform this operation on the NACL page. To do this, go to the Information tab and click Delete.
Attention
The default network access control list cannot be deleted.
Working with rules#
Each network access control list contains numbered inbound and outbound rules that allow or deny traffic at the subnet level. The rules are applied in order of priority, which in turn depends on the number: the lower the number, the higher the priority of the rule. We recommend that you first create rules with numbers that are multiples of 100. This will help you avoid difficulties later when adding rules with an intermediate priority between two existing rules. The highest number a rule can have is 32766.
Attention
One network access control list cannot contain two rules of the same direction with the same number.
Create a rule#
Go to Virtual machines Security Network ACL.
Find the NACL in the resource table and click its ID to go to the NACL page.
Open the required Inbound rules or Outbound rules tab and click Add.
In the window that opens, set the required parameters:
Rule number.
Rule type.
Protocol — You can set the rule for all protocols or select a specific protocol from the list. If there is no required protocol on the list, select
Other.Protocol number — If the protocol is not on the list, set its number according to IANA.
Port access — For TCP and UDP, specify whether all or specific ports can be accessed.
Ports — If you select access to only some ports, specify a comma-separated list of ports and/or port ranges.
Note
A separate rule will be created for each port or port range in the list.
Grant access — You can grant access from all IP addresses or a specified network.
Network — If you select
From Network, specify the network in CIDR notation.
Once all parameters are set, click Add to create a rule.
Once the addition is confirmed, the subnets, which this ACL is associated with, will filter traffic according to the new security rules.
Modify a rule#
Go to Virtual machines Security Network ACL.
Find the NACL in the resource table and click its ID to go to the NACL page.
Open the required Inbound Rules or Outbound Rules tab, select the rule to be modified in the resource list, and click Modify.
In the window that opens, you can edit the following parameters:
Rule number.
Rule type.
Protocol — You can set the rule for all protocols or select a specific protocol from the list. If there is no required protocol on the list, select
Other.Protocol number — If the protocol is not on the list, set its number according to IANA.
Port access — For TCP and UDP, specify whether all or specific ports can be accessed.
Ports — If you select access to only some ports, specify a comma-separated list of ports and/or port ranges.
Note
A separate rule will be created for each port or port range in the list.
Grant access — You can grant access from all IP addresses or a specified network.
Network — If you select
From Network, specify the network in CIDR notation.
Once the parameters are edited, click Change to save the rule.
Once the changes are confirmed, subnets, which this ACL is associated with, will filter traffic according to the new security rules.
Delete a rule#
Go to Virtual machines Security Network ACL.
Find the NACL in the resource table and click its ID to go to the NACL page.
Open the required Inbound rules or Outbound rules tab, select the rule(s) to be deleted in the resource list, and click Delete.
In the window that opens, confirm the deletion.
Information about an NACL#
General information about the existing network access control lists can be viewed in the Network ACL subsection. To view all NACLs in the project, select All VPCs in the VPC filter. To display NACLs from a specific VPC, select the required VPC in the filter.
To view detailed information about a specific network access control list, go to Virtual machines Security Network ACL and select the required list.
To make it easier to find an NACL in the table, you can select the VPC in which the NACL was created in the VPC filter, or use the table search.
After you select the required network access control list, click its ID. The NACL page will open.
The Information tab displays the main NACL characteristics:
ACL name (Name tag);
NACL status as the default network access control list (Yes/No);
VPC where the ACL was created;
number of subnets with which the ACL is associated.
Here you can:
modify ACL name (Name tag);
The Inbound rules tab displays a table with details of inbound rules:
rule number;
protocol;
CIDR block of IP addresses from which access is allowed;
ports;
rule-triggered action.
Here you can add, modify, or delete an inbound rule.
The Outbound rules tab displays a table with details of outbound rules:
rule number;
protocol;
CIDR block of IP addresses to which access is allowed;
ports;
rule-triggered action.
Here you can add, modify, or delete an outbound rule.
The Subnets tab displays a table with details of the subnets to which this NACL is assigned:
subnet ID;
subnet name;
CIDR block of IP addresses;
whether it is a default subnet (Yes/No).
Here you can also assign the NACL to subnets.
On the Tags tab, you can view the tags assigned to the NACL. Here you can also add, modify, and delete tags.